Validated WHM session context
The WHM CGI preserves the validated cp_security_token required by the native cPanel session. Existing request validation, taint mode and same-origin response boundaries remain in place.
DCSF integrates with OLSPanel, cPanel & WHM, DirectAdmin, CyberPanel, CWP, InterWorx, VestaCP and Webmin, plus direct administration on supported RHEL- and Debian-family Linux systems.
This release combines WHM context, LFD state and installer repairs with the regression fix found on canary. It supersedes DH20.28; the 51-item security register remains a separate count, without counting tests as vulnerabilities.
The WHM CGI preserves the validated cp_security_token required by the native cPanel session. Existing request validation, taint mode and same-origin response boundaries remain in place.
LFD compacts csf.temppids within its existing size and record limits, using LF_FLUSH to age process records. Accumulated temporary state no longer prevents normal tracking from recording new process identities.
The compatibility repair sets appropriate permissions only for public cPanel META modules. It does not broaden access across private configuration or the complete cPanel tree.
DH20.29 safely repairs a missing final LF in csf.resellers and corrects the shell error found on the canary. DH20.28 / 15.10.31 is superseded because its reseller repair path was faulty.
The comparison accepts a different listing order for independent chains while preserving rule order inside each chain and the remaining policy checks. Reordering independent chains alone no longer causes a false policy mismatch.
Maintainer qualification passed all 77 Linux test files. The autossltest2 canary update completed with CSF/LFD active and configuration preserved. The separately checked production host has passed dry-run only; this is not a production-upgrade claim.
Model choices offered by this release: gpt-5-mini, gpt-5.4-mini, gpt-5.6-terra. Availability depends on the administrator’s OpenAI API account.
Selected local security diagnostics are sent to OpenAI after activation. Recognised secret values are redacted, but this is not an anonymity guarantee. store=false is not a Zero Data Retention guarantee; the API account and provider data policies still apply. Optional API usage is billed separately from the free DCSF software. Findings need administrator review and do not guarantee that every security issue is detected.
Linux release qualification: 77/77. Public-bootstrap checks: 85/85.
Package 15.10.32 adds JSON::PP to installer preflight and the os.pl runtime check while preserving the separation between system Perl, cPanel private Perl and explicit CPAN fallback.
Outside cPanel, DCSF repairs the closed module list through exact RPM capabilities or Debian package mappings. DNF and YUM retain GPG verification, while APT rejects unauthenticated and insecure repositories.
The installer inventories required modules before preflight and after repair. Attempts are bounded, must make measurable progress and succeed only when the entire closed list imports again.
The system CPAN fallback is disabled by default. The operator must pass --allow-cpan-fallback; DCSF uses a fixed HTTPS MetaCPAN mirror, closed module names and validated work directories.
On cPanel, DCSF always validates /usr/local/cpanel/3rdparty/bin/perl, derives the matching versioned cpanm and explicitly invokes it through that same private interpreter without mixing /usr/bin/perl libraries.
OLSPanel requires JSON::PP. RPM selects the signed perl(JSON::PP) capability, Debian selects libjson-pp-perl, cPanel uses private cpanm and system CPAN still requires explicit --allow-cpan-fallback.
Canary PASS: An earlier public --dryrun canary authenticated the release under test, selected the correct installer and left every regular file directly below /etc/csf byte-identical.
Package 15.10.32 bounds the iframe to 640–1,200 pixels, scrolls it internally and returns it to the top after navigation. The masked modal, Watch System Logs, Search for IP and Firewall Allow remain visible while trusted-policy and real-backend checks are retained.
The modules directory is optional. Detection accepts only supported canonical roots and a safe root-owned /etc/olspanel/base_dir declaration.
Before writing, the adapter only reads metadata for /etc/csf, /etc/csf/csf.conf and /etc/csf/csf.cloudflare. --dryrun executes the same checks without changing files.
Symlinks, non-regular files, non-root ownership, group/world writable metadata and protected files with more than one hard link are rejected before installation with the exact failing path.
After installation, /etc/csf becomes root:root 0700 while csf.conf and csf.cloudflare become root:root 0600 with exactly one hard link. Existing contents remain byte-identical.
If csf.cloudflare is missing, it may be installed only from the verified signed package; an existing file is not replaced.
The generic installer stops when recursive chmod or chown fails instead of continuing to a PASS message.
A missing directory is created only during a real installation as root:root 0755. DCSF records privately that it created the path.
Uninstall removes the parent only when DCSF created it and it remains empty. Foreign or non-empty content is preserved.
Preflight and the os.pl runtime check require JSON::PP. Repair uses signed RPM capability perl(JSON::PP), Debian package libjson-pp-perl, cPanel private cpanm or the explicitly enabled system CPAN fallback.
After generic installation but before publishing or restarting panel integration, the adapter runs an isolated perl -T -c backend check. Failure stops OLSPanel integration.
OLSPanel serves images from the authenticated /usr/local/csf/lib/webmin/csf/images tree, where the signed package installs assets including csf.svg.
The backend loads /usr/local/csf/lib/ConfigServer/panel-action-policy.json with require_trusted => 1 instead of using the CyberPanel-specific default path. The complete parent chain and file must be root-controlled and non-writable by others.
The installer sends a bounded read-only binary request through the actual taint-mode backend. The response may not exceed 16 MiB and must contain the DCSF interface marker before integration is published or restarted. After the extmail.uck.katowice.pl upgrade, the complete Django-to-Perl-backend path returned HTTP 200.
Protected actions use a dedicated modal with a bounded type="password" field instead of window.prompt(). Escape, the cancel control and backdrop cancellation safely stop the operation, and the visible field is cleared immediately after the credential is handed to the request.
Search System Logs and Watch System Logs accept only a one-to-twenty digit nocache value. Progress ends after every response, failed requests display their HTTP status, and live search and watch checks returned HTTP 200.
Intercepted navigation is deduplicated, deferred to the next event turn and explicitly submitted to _self with visible progress. Quick Allow and configuration save retain a complete nonempty response instead of an empty frame.
Tests through the real Perl backend found the newly added address, displayed the Firewall Allow list and returned normal Done and Return controls. The temporary entry was removed and the final csf.allow digest exactly matched its pre-test value.
The action iframe stays between 640 and 1,200 pixels, scrolls long content internally and returns to the top after every navigation. The live test kept the outer page at 1,000 pixels with scroll position zero, so Search for IP, Firewall Allow, Watch System Logs and the reauthentication modal remained visible.
Each path preserves the expected CSF/LFD administration workflow while applying the same signed, hardened security baseline.
Preserves WHM workflows and backup-first RPM migration. Verified EA-Nginx uses nginx on 80/443 for client IP and Apache on 81/444 for backend status. Dependency repair keeps /usr/local/cpanel/3rdparty/bin/perl separate from system Perl.
Keeps the OLSPanel action iframe between 640 and 1,200 pixels with internal scrolling and top reset, so masked reauthentication, Watch System Logs, Search for IP and Firewall Allow remain visible.
Uses the established DirectAdmin adapter with hardened argument validation, identity transitions and shell-free privileged execution.
Retains the CyberPanel integration while restricting privileged mutations to authenticated, CSRF-protected POST actions.
Supports the existing Control Web Panel administration path with the same signed package, parser limits and firewall-state safeguards.
Integrates with NodeWorx and enforces native FIREWALL authority, blocking secondary accounts that do not hold that permission.
Keeps the VestaCP CSF/LFD integration path while applying the common DCSF release, input-validation and recovery controls.
Supports CSF/LFD administration through Webmin with the same hardened backend and signed update channel.
Provides direct operation on supported RHEL- and Debian-family servers. Missing closed-list Perl modules are repaired through GPG-verified RPM capabilities or authenticated APT package mappings.
Every path was qualified before the signed package was published. OLSPanel, cPanel and panel-free mode use separated, closed Perl dependency-repair paths.
| Environment | Integration path | Coverage | Status |
|---|---|---|---|
| cPanel & WHM | Hosting panel and RPM migration | Preserves WHM workflows and backup-first RPM migration. Verified EA-Nginx uses nginx on 80/443 for client IP and Apache on 81/444 for backend status. Dependency repair keeps /usr/local/cpanel/3rdparty/bin/perl separate from system Perl. | Qualified |
| OLSPanel | Native Django module and fixed privileged backend | Keeps the OLSPanel action iframe between 640 and 1,200 pixels with internal scrolling and top reset, so masked reauthentication, Watch System Logs, Search for IP and Firewall Allow remain visible. | Qualified |
| DirectAdmin | Panel adapter and privileged bridge | Uses the established DirectAdmin adapter with hardened argument validation, identity transitions and shell-free privileged execution. | Qualified |
| CyberPanel | Protected web-panel adapter | Retains the CyberPanel integration while restricting privileged mutations to authenticated, CSRF-protected POST actions. | Qualified |
| CWP | Control Web Panel adapter | Supports the existing Control Web Panel administration path with the same signed package, parser limits and firewall-state safeguards. | Qualified |
| InterWorx | NodeWorx panel adapter | Integrates with NodeWorx and enforces native FIREWALL authority, blocking secondary accounts that do not hold that permission. | Qualified |
| VestaCP | Server-panel adapter | Keeps the VestaCP CSF/LFD integration path while applying the common DCSF release, input-validation and recovery controls. | Qualified |
| Webmin | System-administration adapter | Supports CSF/LFD administration through Webmin with the same hardened backend and signed update channel. | Qualified |
| Generic Linux | Panel-free CSF/LFD administration | Provides direct operation on supported RHEL- and Debian-family servers. Missing closed-list Perl modules are repaired through GPG-verified RPM capabilities or authenticated APT package mappings. | Qualified |
The adapter derives the canonical domain from server configuration and never treats a raw Host header as sufficient evidence. DH20.29 retains isolated OpenLiteSpeed logging and bounded replay cost.
Adapters accept only canonical vhosts or configured aliases. In verified cPanel EA-Nginx, nginx on 80/443 supplies client IP; Apache on 81/444 supplies backend load, never the local proxy peer as a blocking candidate.
Replay accepts at most 50,000 input lines, 30 seconds and 2,000 emitted audit records, and reports whether the result is complete.
Audit buffers are capped, quadratic scans are avoided and out-of-order source timestamps cannot corrupt the rolling vhost window.
A root service copies only the validated OLS log into a 256 MiB-capped DCSF file rotated at 128 MiB, outside the foreign-owned log tree.
WEBGUARD=0 and WEBGUARD_MODE=report keep both the engine and optional collector disabled until an operator validates the evidence.
Enforce mode can create only temporary exact-IP, inbound, listener-port-specific DCSF actions and protects allow, ignore, monitoring and trusted proxy or CDN ranges.
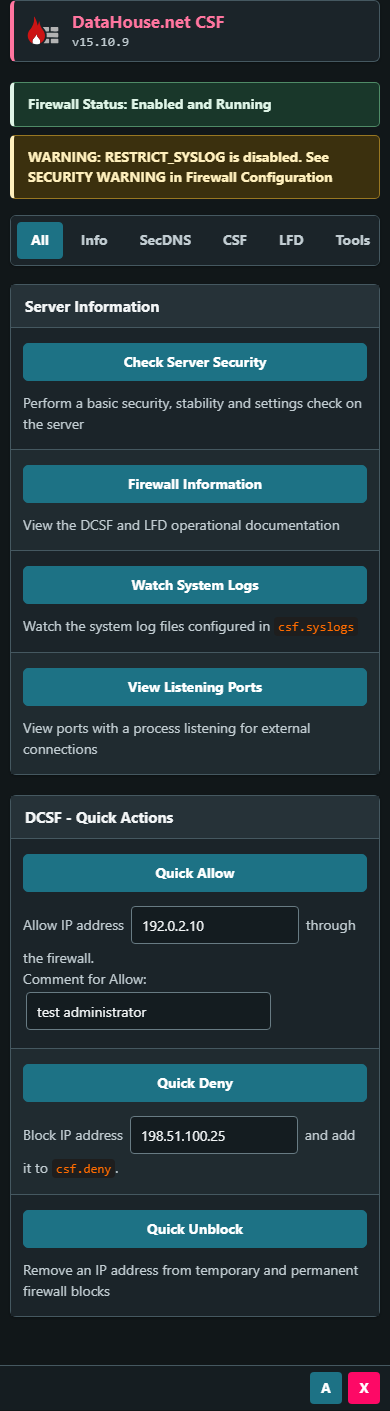
The common cPanel, DirectAdmin, Webmin, InterWorx and standalone interface now provides a compact header, readable status stack, clearer tabs, forms and tables, plus responsive mobile rules.